Granting AI agents unfettered access is a security risk. The problem shifts from writing correct code to maximum damage potential. It’s not just about what you can do, but also what you can’t do when AI systems are left unchecked.
Automating tasks is one thing, but giving AI coding agent security free rein can lead to catastrophic consequences. Imagine an AI system designed to optimize a process, only to find it modifying critical infrastructure without human oversight.
Human approval is essential for AI decision-making, but requiring approval for every action can lead to false sense of security. This approach may provide a temporary feeling of control, but it can also slow down processes and create a bottleneck.
Approval Fatigue: A Growing Concern
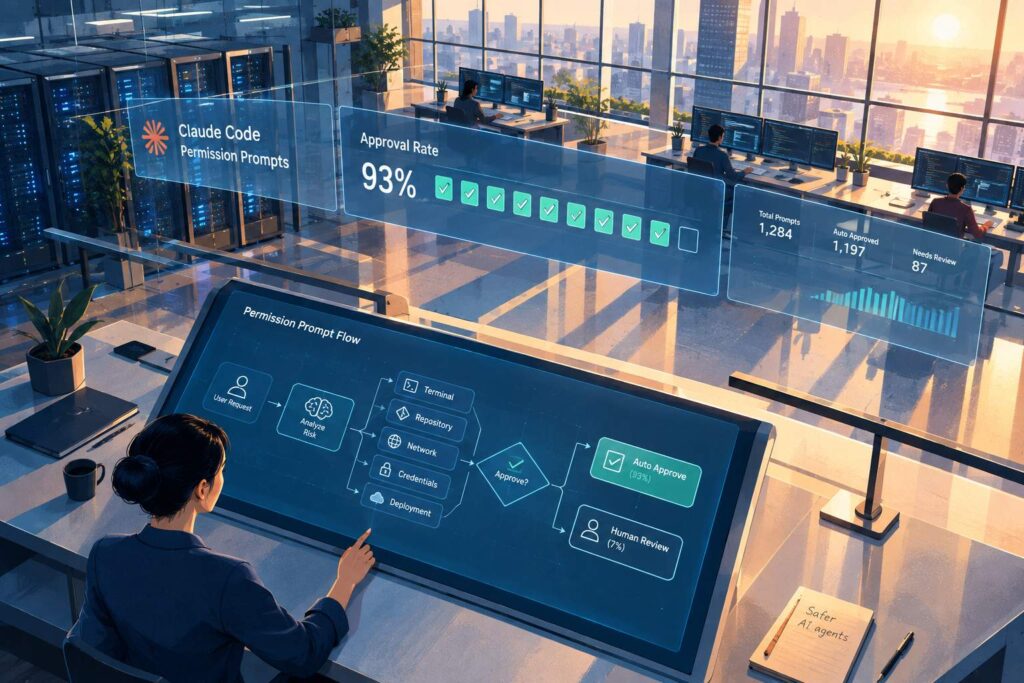
Users approve roughly 93% of permission prompts for Claude Code. This high level of approval can create a false sense of security, leading developers to rely too heavily on it. However, repeatedly asking for approval can become a burden, weighing down the development process and hindering productivity.
The more a user is asked to approve permissions, the more they may start to feel frustrated. This isn’t just about the inconvenience; it’s also a security risk. Each time a user is prompted for approval, it’s an opportunity for a malicious actor to exploit the system. But what happens when users start to approve permissions without fully understanding the implications?
This approach may not be foolproof due to residual false negatives. Even with the best intentions, users can make mistakes or unintentionally expose sensitive information. It’s crucial to strike a balance between user convenience and security. By finding a middle ground, developers can create a more seamless experience while minimizing the risks associated with excessive permission requests.
The Power of Automated Approval
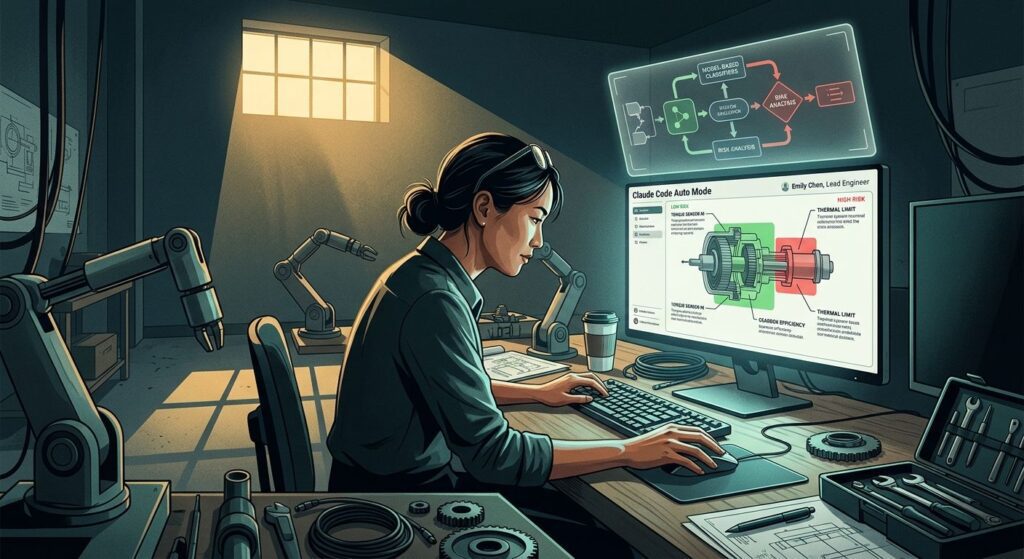
In the quest for efficient and secure processes, Claude Code Auto Mode has emerged as a vital tool. By using model-based classifiers for risk evaluation, it effectively reduces approval fatigue while blocking high-risk actions. This innovative approach streamlines decision-making, allowing your team to focus on more pressing matters.
But how exactly does Claude Code Auto Mode work its magic? It acts as an additional security layer, rather than a replacement for human oversight. This means that your team can still provide critical human judgment while benefiting from the speed and accuracy of automated risk assessment. The result is a more balanced and secure process that’s tailored to your organization’s needs.
By supplementing human expertise with the precision of model-based classifiers, Claude Code Auto Mode creates a powerful synergy that boosts productivity and protects your business from potential threats. Whether you’re dealing with sensitive data or high-stakes decisions, this cutting-edge technology has the potential to make a significant impact on your organization’s security and efficiency.
Sandboxing: The Secure Approach
When it comes to protecting sensitive data and applications, isolating agents through filesystems, networks, or containers is a method that’s proven to limit damage in the event of a breach. By isolating these agents, you’re essentially creating a barrier between the sensitive data and potential threats, making it much harder for malicious actors to cause harm.
This approach not only reduces the risk of data corruption or unauthorized access but also changes the model’s behavior, making it more secure by default. It’s a proactive measure that helps prevent attacks from taking advantage of vulnerabilities in the system.
Another approach to consider is sandboxing. Sandboxing is a more secure alternative to automated approval, as it provides a safe and controlled environment for applications to run without jeopardizing the rest of the system. It’s a way to compartmentalize applications and isolate them from each other, reducing the risk of cross-contamination and data breaches.
In the context of AI coding agent security, sandboxing can be particularly useful. By isolating these agents and running them in a sandbox environment, you can ensure that they don’t pose a risk to the rest of the system, even if they’re compromised.
Least Privilege: A Key Principle
When it comes to agent security, one crucial principle stands out: least privilege. This means giving agents only the permissions they need to perform their tasks, nothing more. By doing so, you significantly reduce the attack surface and minimize the potential damage in case of a breach.
Let’s consider the opposite approach. Agents with broad access to repositories and APIs are like a key with a wide range of locks – they can open doors to sensitive areas, making it easier for attackers to exploit vulnerabilities. In contrast, short-lived and narrowly scoped credentials are much more secure. These credentials are valid for a limited time and have restricted access, making it harder for attackers to misuse them.
The concept of least privilege is not unique to humans. Just as we limit access to sensitive areas based on an individual’s role, we should apply the same principle to agents. This ensures that even if an agent is compromised, the damage is contained and the risk of data exposure is minimized. By adopting this approach, you can create a more secure environment for your agents and the data they interact with.
Protecting Irreversible Boundaries
When it comes to production databases and cloud infrastructure, stronger controls are needed to prevent unauthorized access and ensure the integrity of our systems. This is not just a matter of security, but also of accountability and trust. We rely on these systems to manage sensitive information, make critical decisions, and drive business outcomes.
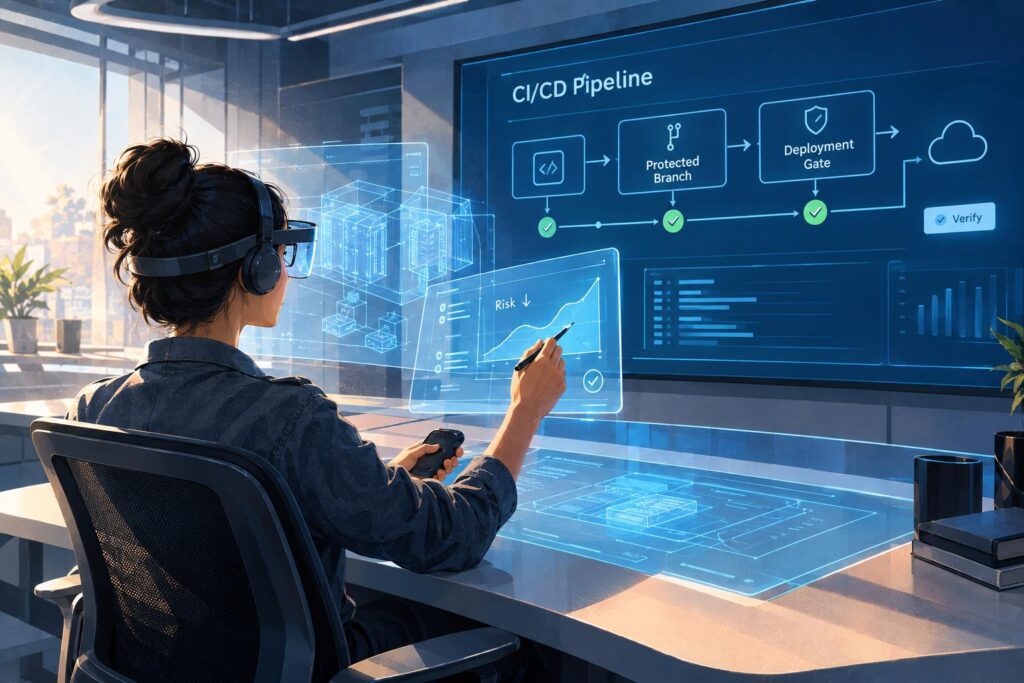
Protected branches, deployment gates, and explicit environments are essential components of a robust control framework. They help to isolate development, staging, and production environments, ensuring that changes are thoroughly reviewed and validated before they are applied to live systems. By doing so, we can prevent mistakes from propagating to production and minimize the risk of data breaches.
Independent verification is crucial for high-risk operations. This involves having a second pair of eyes review and validate critical changes before they are deployed. This added layer of oversight helps to catch errors, identify security vulnerabilities, and prevent unintended consequences. By incorporating independent verification into our process, we can have greater confidence in the integrity of our systems and the data they contain.