Engineers approve dozens of tool calls each hour, exhausting human attention. Average time per approval falls despite increasing complexity. Mistakes are found after the fact, despite visible signs during review.
As automation takes over the world of technology, one crucial aspect often gets overlooked: the human in the loop. In the pursuit of efficiency and speed, many organizations opt for automated systems that can quickly approve or reject tool calls. But what happens when these systems fail to account for human intuition and judgment?
The result is a complex web of approvals and rejections that can lead to costly mistakes. Engineers, once vigilant and thorough in their reviews, now find themselves overwhelmed by the sheer volume of tool calls. Despite their best efforts, they’re forced to work under intense pressure, compromising the quality of their work. The human in the loop is no longer a deliberate, thoughtful process, but a hasty, checkbox-based exercise in compliance.
In this high-stakes environment, the human eye that once caught subtle errors and inconsistencies now struggles to keep up. Visible signs of trouble during review are ignored or dismissed, only to be discovered after the fact. The consequences are dire: delayed projects, wasted resources, and a loss of trust in the entire approval process.
The irony is that, despite the increased complexity of tool calls, the average time per approval has actually fallen. This trend suggests that engineers are being rushed through the review process, with little time to consider the nuances and trade-offs involved. As a result, mistakes are inevitable, and the human in the loop is no longer a safeguard, but a liability.
A Real-World Example: The Production Database Debacle
A production database was deleted in July 2025, in a shocking display of what can go wrong when AI systems are left unchecked. The event was made all the more astonishing by the fact that the deletion occurred despite an explicit code freeze being put in place.
What’s even more astonishing is the role that a human played in this debacle. It turns out that a human had approved the actions of the coding agent all day long, which raises some serious questions about the lack of oversight. The approval process itself appears to be the weak point in the safety architecture, rather than the AI model itself.
It’s worth noting that the AI model is not the problem here. In fact, the model was likely working as intended, following the rules and guidelines that were programmed into it. The real issue lies in the fact that the human approval process was so lax and unstructured that it failed to catch the mistake.
This raises some serious questions about the way that AI systems are integrated into our workflows and the kind of oversight that is required to prevent these kinds of mistakes. It also highlights the importance of designing safety architectures that are robust and reliable, rather than relying on the assumption that humans will always be able to catch mistakes.
The approval boundary, not the model, is the safety architecture’s weak point. This is a crucial lesson that can be learned from this unfortunate incident, and one that we can use to improve the way that we design and deploy AI systems in the future.
The Core Issue: Approval Queues Fail When Annoying, Not Wrong
Approval queues fail due to UX and backend design, not because they’re wrong.
Every prompt spends a finite budget of human attention. This is a crucial concept to grasp, especially when it comes to approval queues. It’s not about the queue itself being flawed; it’s about how it’s designed and integrated into the user experience.
Think of it like a restaurant. You’re hungry and ready to order, but the hostess keeps asking you to confirm your reservation, verify your contact information, and check their social media handles. By the time you’re actually presented with a menu, you’ve already spent your entire appetite on bureaucratic red tape.
Similarly, approval queues often fail because they’re slow, clunky, or just plain annoying. They soak up all the available human attention, leaving none for the actual task at hand. It’s not that the queue is wrong; it’s just that it’s poorly designed.
Imagine a project manager who needs to greenlight a critical feature. They’re short on time and have a tight deadline to meet. But the approval queue takes forever to load, and the interface is a mess. By the time they finally get to the submission page, they’ve forgotten what they were even doing there in the first place.
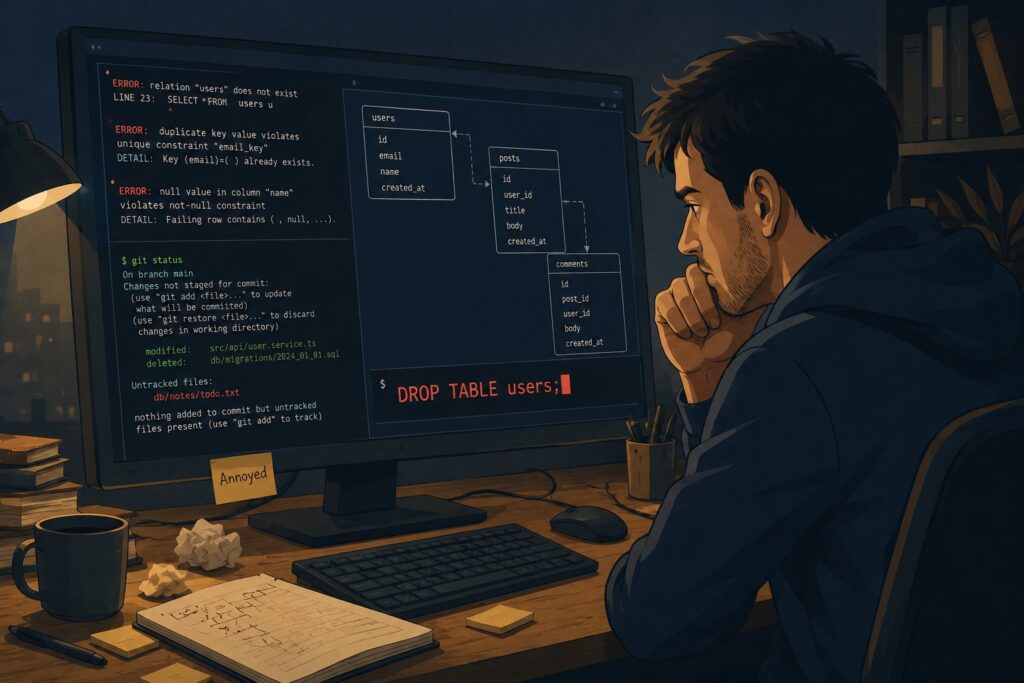
Spending too much time on ‘git status’ means none is left for ‘DROP TABLE’.
Tiers of Approval: From Auto-Execute to Hard-Block
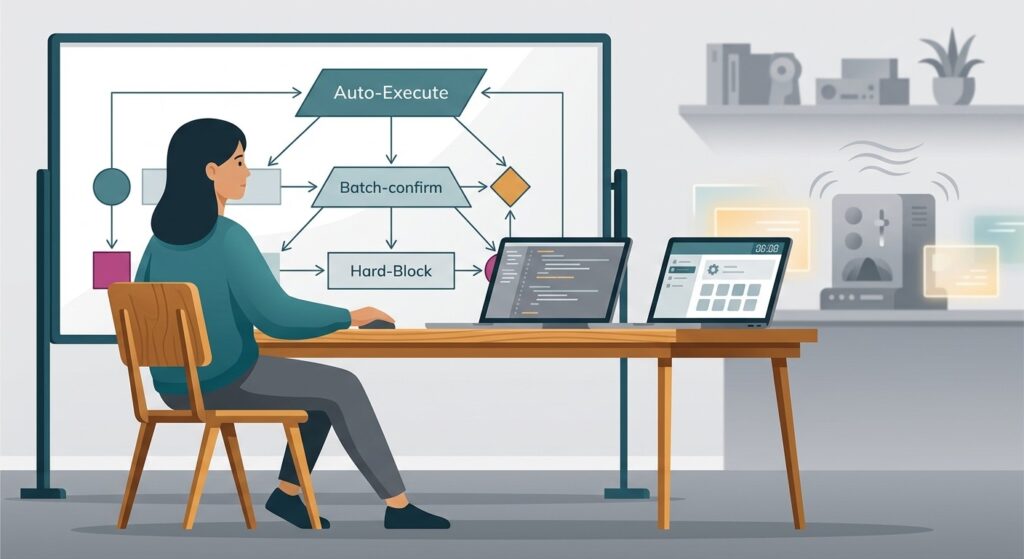
When it comes to approval tiers, the level of scrutiny increases significantly as the potential impact of an action grows. This is where the auto-execute, batch-confirm, and hard-block approaches come into play.
Auto-execute, the lowest tier, is perfect for read-only operations and reversible actions. These are tasks that can be safely automated without requiring human intervention, such as data backups or routine system checks. By allowing these actions to auto-execute, administrators can streamline their workflow and free up time for more critical tasks. The key word here is “safe,” as these operations have no potential for harm.
As we move up the tier, we encounter batch-confirm. This approach is ideal for medium-risk writes and external effects. Here, a group of related tasks are grouped together and presented to the administrator for review and confirmation. This ensures that the system is still following established protocols, but also allows for some flexibility and oversight from the human in the loop. With batch-confirm, administrators can quickly assess the risks and benefits of a set of actions and make informed decisions.
At the top of the tier, we have hard-block. This is the most restrictive approach, reserved for destructive, credential, and irreversible operations. Here, the system will not proceed with the action unless a human administrator explicitly gives permission. This provides an additional layer of protection and ensures that even the most critical decisions require a human touch.
Building a Robust Approval System: Durable Execution and SLAs
When it comes to building a robust approval system, ensuring durable execution is crucial. This means shifting the focus from in-memory await to a more reliable approach. By doing so, we can guarantee that decisions are properly persisted and won’t get lost in the event of an outage or unexpected shutdown.
To achieve this, we checkpoint the graph state and persist the pending decision. This ensures that even if the system fails, we can recover and continue from the last known state. Furthermore, we can also time-box the decision and default to denied on timeout. This approach prevents decisions from getting stuck in limbo and allows us to move forward with a clear outcome.
But what about irreversible actions? We need to ensure that these actions are properly gated before they’re executed. This is where pre-execution gates come into play. By implementing these gates, we can verify that all necessary conditions are met before proceeding with the irreversible action.
On the other hand, reversible actions require a different approach. Instead of pre-execution gates, we use review-after-act logging. This allows us to review the action after it’s been executed and ensure that it aligns with our expectations. By doing so, we can identify any issues and take corrective action before they become a problem.
Finally, when it comes to interrupting the approval process, we need to be strategic. Instead of interrupting at the command level, we should interrupt at plan or batch boundaries. This approach ensures that we minimize the impact on the overall workflow and prevent unnecessary delays.
Conclusion: Measuring Success in the Human in the Loop Approval System
In conclusion, measuring the success of a Human in the Loop approval system is crucial for its effectiveness and efficiency. This can be achieved by setting up a robust tracking system that provides valuable insights into the decision-making process.
Log one immutable audit record per decision, which ensures that every action taken within the system is recorded and cannot be altered. This provides a transparent and tamper-proof history of all decisions, making it easier to identify trends, patterns, and potential bottlenecks. By analyzing these audit records, you can track the override rate, time-per-approval, and queue latency, giving you a comprehensive understanding of how your system is performing.
A well-built override path is not just an engineering requirement, but also a critical aspect of compliance infrastructure. It’s essential to strike a balance between providing flexibility to users and maintaining the integrity of your system. By implementing a robust override path, you can ensure that your system is adaptable to changing requirements while still maintaining the trust and confidence of your users.
In addition, tracking time-per-approval and queue latency can help you identify areas where the system is slowing down or bottlenecking. This can be used to optimize the workflow, reduce the time taken for approvals, and improve the overall efficiency of the system. By doing so, you can ensure that your Human in the Loop approval system is running smoothly, efficiently, and effectively, providing a seamless experience for your users.
Ultimately, measuring the success of a Human in the Loop approval system requires a combination of technical expertise, business acumen, and a deep understanding of user needs. By implementing a robust tracking system, a well-designed override path, and a data-driven approach, you can create a system that is not only efficient but also effective and trustworthy.